Procore Integration: Installation
Install the OAuth/DMSA connector, connect projects, and review the requested permissions.
Overview
LiveArch's Procore integration brings assigned RFIs and Submittals into LiveArch for design-team coordination and returns the finalized response to Procore. The LiveArch x Procore connector uses industry-standard OAuth and a Procore Developer Managed Service Account (DMSA), connecting as an authorized Procore application whose access is scoped to the company- and project-level permissions your Procore administrator approves, and enforced by Procore itself. Once installed, see Linked RFIs and Linked Submittals for the day-to-day workflow rules.
Installation normally takes about five minutes once the required Procore access is available. Procore's own walkthrough of custom-app installation is at Install a Custom App (Procore Support).
Install the connector
Before installing, confirm you have permission in Procore to install and configure apps.
The current LiveArch App Version ID is
2904577f-57b4-4167-a0dc-0cb22c34a7d6.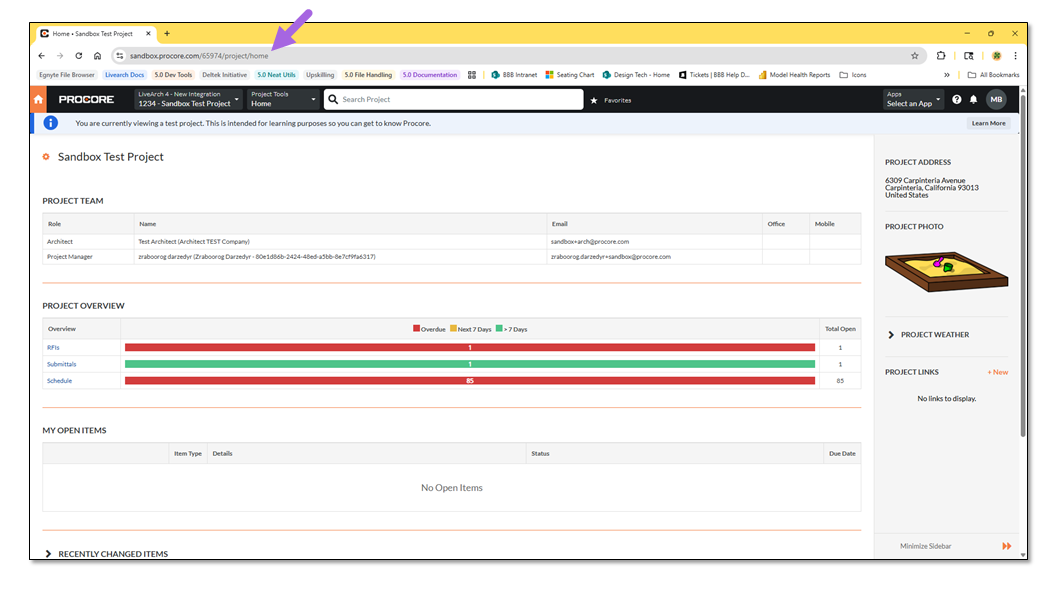
1 / 7
After installing the LiveArch x Procore integration
The remaining setup is handled in LiveArch; reach out to the project team to advise them the connector is installed on the project. It is also recommended to schedule a short kick-off call for all projects, to ensure alignment on workflow expectations and run a quick connectivity test.
Requested permissions
The LiveArch connector's access to Procore is governed entirely by the pre-authorized permissions below, which Procore enforces at the API level — the application cannot read or modify any Procore data it hasn't been explicitly authorized to access, even if it were compromised or malfunctioning. Procore's permissions manifest covers both company-level and project-level tools; the table below lists the project-level tools requested, and which specific projects can connect is controlled separately by your Procore company administrator. LiveArch cannot expand its own access — any permission change ships as a new app version, which a Procore company administrator must independently review and explicitly approve, including any new permissions, before it takes effect. This least-privilege model means the connector can never compromise the security or integrity of Procore or its data.
| Permission name | Access level | Required for |
|---|---|---|
| Directory | Standard | Confirm Support access and identify the project user that represents the LiveArch Integration. |
| Document Management | Standard | Reads the project drawings, specifications, and other documents linked to RFIs or Submittals. |
| Documents | Standard | Reads the project drawings, specifications, and other documents linked to RFIs or Submittals. |
| Drawings | Standard | Reads the project drawings, specifications, and other documents linked to RFIs or Submittals. |
| RFIs | Standard | Reads assigned RFIs and writes back the finalized response. |
| Specifications | Standard | Reads the project drawings, specifications, and other documents linked to RFIs or Submittals. |
| Submittals | Standard | Reads assigned Submittals and writes back the finalized response. |
| Webhooks API | Admin | Allows LiveArch to create webhooks in Procore. Procore uses webhooks to notify LiveArch automatically when an RFI or Submittal record is created or updated. Configure Webhooks (Procore Support) |
Uninstalling or disabling the connector
A Procore company administrator can limit or terminate the connector's access at any time, independent of LiveArch — by removing a project from the app's permitted list, declining a requested permission update, or uninstalling the app entirely from Procore's App Management. Coordinate with the BBB project team first: removing access stops the sync for that project, and any RFIs or Submittals still in progress will need to be handled manually.
Support
Questions or issues? We're happy to help — , or use the contact form if you're signed out.